TL;DR
- Steaelite: A commercial RAT-as-a-service with automated browser credential harvesting, a web-based operator panel, and an integrated ransomware module.
- Blackreaper: A remote access trojan attributed to the Forbidden Hyena group, implemented in VBScript, controlled via a Telegram channel, and capable of spreading through removable media.
- Jigsaw: Ransomware that disguises itself as svchost.exe, encrypts files, and demands a ransom.
1) Steaelite (Windows)
Sample: ANY.RUN
Steaelite is a commercial remote access trojan (RAT) offered as part of a malware-as-a-service model and sold to cybercriminals. It combines automated browser credential harvesting with a web-based operator panel and built-in ransomware capabilities.
How it was detected
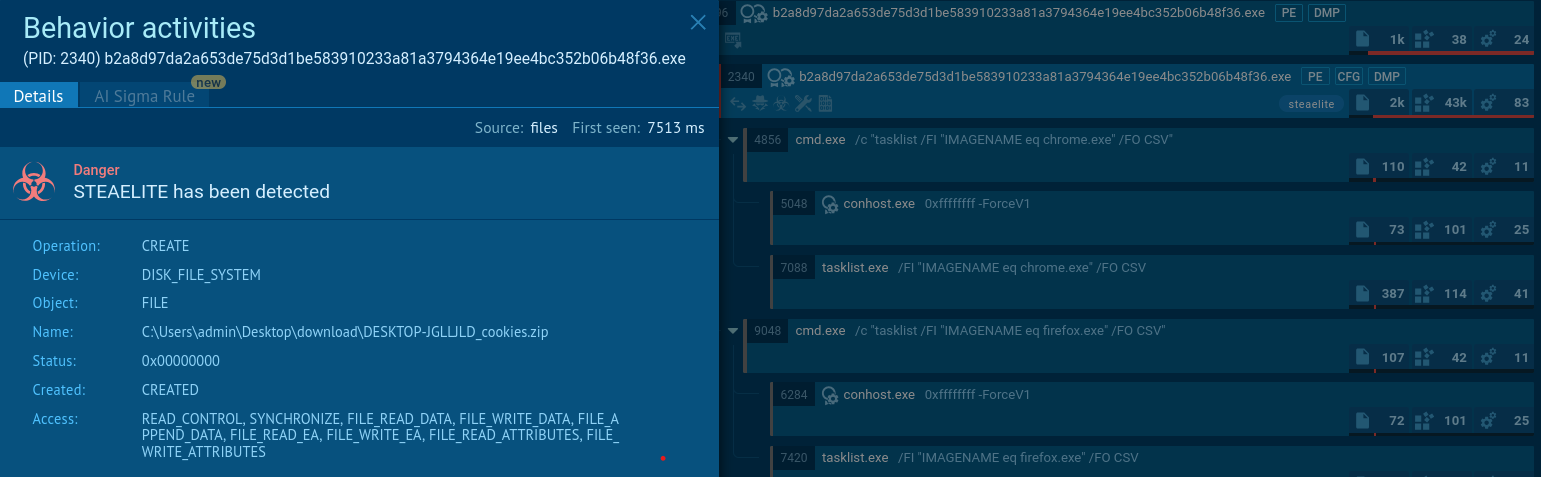
Detection is based on the ZIP archive artifact in the temporary directory with a path matching the regex C:\Users\\AppData\Local\Temp\SK_\d{8,14}.zip, as well as the creation of a Desktop-*_cookies.zip archive.
Malware features
- Distributed via subscription on forums and Telegram.
- Automatically collects browser cookies and credentials upon initial infection.
Analytical notes
| Detected | External sources | ANY.RUN Last Submission | Sandbox Evasion |
|---|---|---|---|
| 2026-02-26 | broadcom.com | 2026-03-03 | 2 |
With the following TI Lookup query, we can search through recent public sandbox analyses and identify this malicious activity.
TI Lookup:
filePath:"C:\\Users\\admin\\*\\download\\DESKTOP*_cookies\.zip"
IOCs:
- SHA256:
b2a8d97da2a653de75d3d1be583910233a81a3794364e19ee4bc352b06b48f36
MITRE:
| Technique ID | Technique Name | Evidence |
|---|---|---|
| T1555.003 | Credentials from Web Browsers | Creation and modification of browser cookie files and a ZIP archive containing them. |
| T1041 | Exfiltration Over C2 Channel | Creation of the Desktop-*_cookies.zip archive and upload to cloud endpoints. |
| T1057 | Process Discovery | Execution of tasklist for Chrome, Firefox, Edge and other browsers. |
| T1082 | System Information Discovery | Reading the machine GUID, computer name and time zone. |
2) Blackreaper (Windows)
Sample: ANY.RUN
Blackreaper is a remote access trojan attributed to the Forbidden Hyena group. It is fully implemented in VBScript, distributed within RAR archives using AI-generated loaders, and receives commands from a public Telegram channel, executing them via cmd.exe.
How it was detected
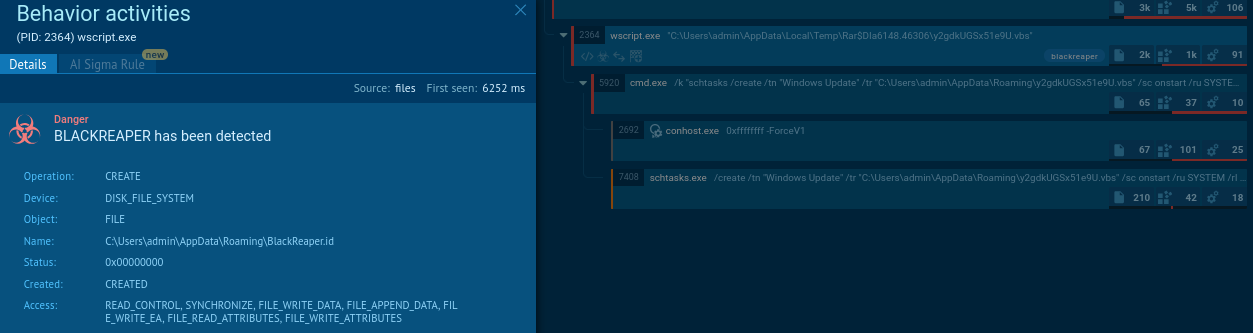
The trojan was identified by the presence of the local artifact file %AppData%\BlackReaper.id, which contains a unique BotID, as well as by command-line activity indicating VBS file deletion.
Malware features
- Communicates with its C2 infrastructure via Telegram.
- Stores a unique BotID and creates a lock file to prevent reinfection or duplication.
Analytical notes
| Detected | External sources | ANY.RUN Last Submission | Sandbox Evasion |
|---|---|---|---|
| 2026-05-03 | News | 2026-02-20 | 4 |
With the following TI Lookup query, we can search through recent public sandbox analyses and identify this malicious activity.
TI Lookup:
filePath:"BlackReaper.id"
IOCs:
- SHA256:
4fbd2f5b4625fa46b5706748dbb15d3f58fbeda723fc644d0db9174a78cbade1 - SHA256:
e8e0df835a3bedb6457ce71f4b114c01c2f4edf1d6332d224921bad5845755b7 - SHA256:
5df07f2b3ddae4b24d05926167a4a5968e2748efe744e4600f968be9abd293a2 - SHA256:
4fbd2f5b4625fa46b5706748dbb15d3f58fbeda723fc644d0db9174a78cbade1
MITRE:
| Technique ID | Technique Name | Evidence |
|---|---|---|
| T1059.005 | Visual Basic | Executes an obfuscated VBS script via wscript.exe or cscript.exe. |
| T1059.003 | Command and Scripting Interpreter: Windows Command Shell | Launches commands via cmd.exe /k [command]&&exit. |
| T1547.001 | Boot or Logon Autostart Execution: Registry Run Keys | Creates Run keys in HKLM or HKCU for autostart of the VBS script. |
| T1547.001 | Boot or Logon Autostart Execution: Startup Folder | Copies the VBS file to the folder %AppData%\Microsoft\Windows\Start Menu\Programs\Startup. |
| T1053.005 | Scheduled Task/Job: Scheduled Task | Creates the “Windows Update” task to run the VBS with SYSTEM privileges. |
| T1071.001 | Application Layer Protocol: Web Protocols | Uses the Telegram channel and HTTPS C2 for commands and exfiltration. |
| T1105 | Ingress Tool Transfer | Downloads payload, updates and additional files from the C2 server. |
3) Jigsaw (Windows)
Sample: ANY.RUN
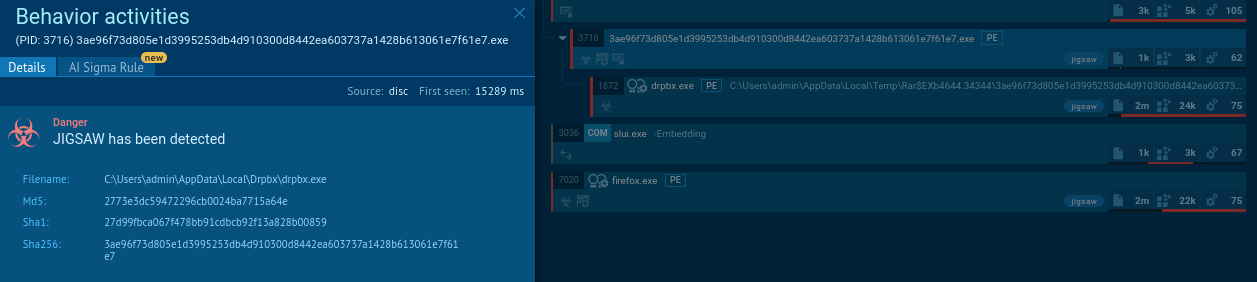
Jigsaw is ransomware that encrypts files and demands ransom for decryption. It uses a malicious executable named svchost.exe to disguise its activity and maintain persistence, dropping it in a directory that mimics a legitimate Windows process.
How it was detected
Detection is based on identifying abnormal file encryption activity.
Malware features
- Masquerades as the legitimate system process svchost.exe.
- Encrypts files and issues a ransom demand.
Analytical notes
| Detected | External sources | ANY.RUN Last Submission | Sandbox Evasion |
|---|---|---|---|
| 2026-03-12 | News | 2026-03-16 | 0 |
With the following TI Lookup query, we can search through recent public sandbox analyses and identify this malicious activity.
TI Lookup:
filePath:".png.fun$"
IOCs:
- SHA256:
245635dac79cc8264ab1ac7dadf014f2dbaeaa56ec8d25bcda4ce6785f5802fe - SHA256:
86a391fe7a237f4f17846c53d71e45820411d1a9a6e0c16f22a11ebc491ff9ff - SHA256:
1be4eb3bcf00e185937ad0340a88b1140270e8e0d93cd6dfa77df388a14351ea - SHA256:
a640420f432c6c047ae196dc5f0e1bfc29d47433087f578386a0c4d9d0e6a3bc
MITRE:
| Technique ID | Technique Name | Evidence |
|---|---|---|
| T1112 | Modify Registry | Modifies registry entries. |
| T1547.001 | Boot or Logon Autostart Execution: Registry Run Keys / Startup Folder | Changes autorun values in the registry. |
| T1497.003 | Virtualization/Sandbox Evasion: Time Based Checks | Reads the date of Windows installation. |
| T1082 | System Information Discovery | Checks various system data. |
| T1486 | Data Encrypted for Impact | Encrypts files. |
Conclusion
Steaelite demonstrates a notable convergence of RAT and ransomware functionality within a single control panel.
The advanced feature set of Steaelite also includes a built-in clipper.
BlackReaper uses an unconventional C2 channel, extracting encrypted commands from the “description” field of a public Telegram channel.
All three threats actively leverage the registry to maintain persistence.