TL;DR
- Maverick (Windows banking trojan): Distributed via WhatsApp campaigns. It steals account data, intercepts traffic, and performs banking operations. Executes only in Brazil (based on IP and system language). Detection via YARA (string Maverick2025 + Brazilian debug strings).
- ChaosBot (Windows, Rust): Uses Discord for C2, employs DLL side-loading, evades VM/ETW detection, and supports remote commands and screenshots.
- Floxif (Windows backdoor): A legacy malware family, but still active; detected via dropped DLL.
1) Maverick (Windows)
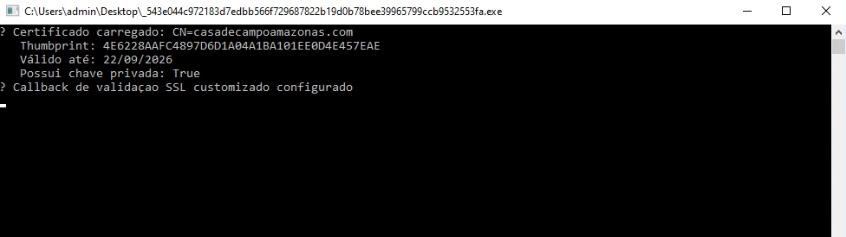
Sample: ANY.RUN
Maverick is a banking trojan distributed via WhatsApp campaigns; steals account data, intercepts traffic, and performs banking actions.
How to detect: YARA string Maverick2025 + Brazilian debug strings.
Key facts:
- Target: Brazil. It executes only if the user’s IP address is Brazil-based and the Windows system language is Portuguese (Brazil).
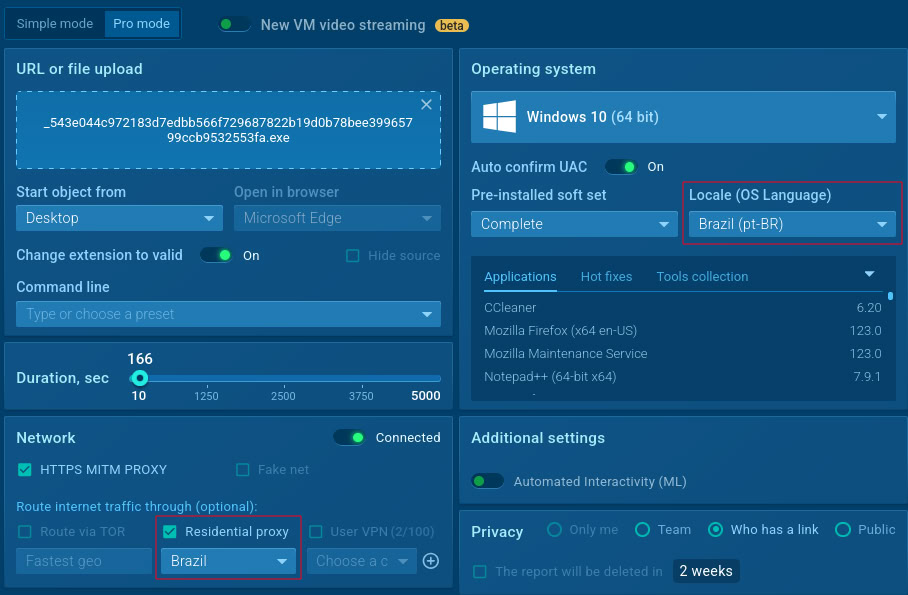
- Delivery via personal WhatsApp messages increases infection conversion and bypasses corporate email hygiene.
Analytical note:
| Detected | External sources | Last Submission to ANY.RUN | Sandbox Evasion | VT First Submission |
|---|---|---|---|---|
| 2025-10-20 | News | 2025-10-14 | 2 | 2025-10-07 |
YARA rule for searching in TI Lookup:
rule Maverick_Banker
{
    meta:
        author = "ANY.RUN"
        description = "Detects Maverick Banker, a sophisticated banking trojan targeting Brazilian users to steal financial credentials and sensitive banking information"
        threat = "maverick"
        tags = "maverick, banker"


    strings:

        $x1 = /Maverick20\d{2}!/ fullword wide
        $x2 = "Maverick.Agent" fullword ascii

        // Brazilian geo-targeting and anti-analysis strings
        $s1 = "IsValidBrazilianTimezone" fullword ascii
        $s2 = "IsBrazilianLocale" fullword ascii
        $s3 = "IsBrazilianRegion" fullword ascii
        $s4 = "IsBrazilianDateFormat" fullword ascii
        $s5 = "AntiAnalysisBrazil" fullword ascii
        // Portuguese language strings (certificate/banking operations)
        $s6 = "Abra o APLICATIVO instalado" fullword wide
        $s7 = "Certificado carregado:" fullword wide
        $s8 = "Possui chave privada:" fullword wide
        $s9 = "ValidateServerCertificate chamado!" fullword wide
        $s10 = "Callback de valida" fullword wide
        $s11 = "Certificado confi" fullword wide
        $s12 = "Certificado recebido do servidor:" fullword wide
        $s13 = "Certificado do servidor validado com sucesso!" fullword wide
        $s14 = "Erro ao validar certificado:" fullword wide
        $s15 = "[Agent] Connected to server, PSK authentication will be handled automatically" fullword wide
        $s16 = "Client desconectado:" fullword wide

    condition:
        uint16(0) == 0x5A4D and
        (
            (any of ($x*) and 4 of ($s*)) or
            (all of ($x*) and 8 of ($s*)) or
            (12 of ($s*))
        )


}
IOCs:
SHA256:
543e044c972183d7edbb566f729687822b19d0b78bee39965799ccb9532553faDomains:
casadecampoamazonas.com,bravexolutions.com
MITRE:
| Technique ID | Technique Name | Evidence |
|---|---|---|
| T1566.001 | Phishing: Spearphishing Attachment | Victim receives malicious .LNK file in ZIP archive via WhatsApp message with filename pretending to be from a bank |
| T1059.001 | Command and Scripting Interpreter: PowerShell | LNK executes cmd.exe to run PowerShell script decoding .NET file in memory by dividing bytes by 174 |
| T1059.007 | Command and Scripting Interpreter: JavaScript | WPPConnect script in “ZAP” namespace automates WhatsApp Web message sending to contacts |
| T1547.001 | Boot or Logon Autostart Execution: Startup Folder | .bat file named “HealthApp-” + GUID + “.bat” stored in C:\Users<user>\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup |
| T1056.001 | Input Capture: Keylogging | KEYLOGGER command enables local key capture and sends logs to C2 on request |
| T1567 | Exfiltration Over Web Service | GENERATEWINDOWREQUEST command creates phishing overlay for banking credentials |
2) ChaosBot (Windows, Rust)
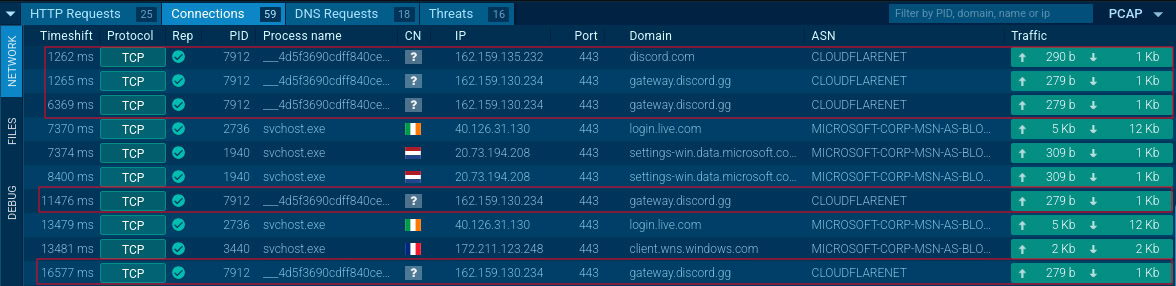
Sample: ANY.RUN
ChaosBot is a new Rust-based backdoor for reconnaissance and remote command execution on Windows. It uses Discord channels as a hidden C2.
How to detect: YARA based on unique anti-VM and ETW evasion patterns.
Key facts:
- Rust + Discord-C2: management via Discord channels complicates interception/attribution.
- DLL side-loading and stealth loading: identity_helper.exe / msedge_elf.dll with thread injection.
- Anti-analysis/monitoring evasion: patching EtwEventWrite, checks for virtual MAC adapters; can upload/download files, take screenshots, execute shell commands.
Analytical note:
| Detected | External sources | Last Submission to ANY.RUN | Sandbox Evasion | VT First Submission |
|---|---|---|---|---|
| 2025-10-13 | News | 2025-10-13 | 5 | 2025-09-22 |
YARA rule for searching in TI Lookup:
rule ChaosBot
{
    meta:
        author = "ANY.RUN"
        description = "Detects ChaosBot - Rust-based malware using Discord for C2 operations with capabilities for command execution, reconnaissance, data exfiltration, and anti-VM/ETW evasion techniques"
        threat = "chaosbot"
        tags = "chaosbot, backdoor"


    strings:
        $bypass = {
            74 ??
            66 C7 03 31 C0
            C6 43 02 C3
        }


        $antivm = {
            48 ?? 30 30 3A 30 43 3A 32 39
            49 39 ?? 00
        }


        $s1 = "Host  connected, channel created: <" fullword ascii
        $s2 = "shell download cd Failed to change directory:" fullword ascii
        $s3 = "VirtualProtectAmsiScanBufferEtwEventWriteCOMPUTERNAME" fullword ascii
        $s4 = "C:\\Users\\Public\\message_.txt" fullword ascii
        $s5 = "Usage: upload <URL> <target_path>" fullword ascii
        $s6 = "C:\\Users\\Public\\screenshot_.png" fullword ascii
        $s7 = "Download failed:" fullword ascii
        $s8 = "File uploaded successfully to:" fullword ascii


    condition:
        uint16(0) == 0x5a4d and (5 of ($s*) and ($antivm or $bypass))
}
IOCs:
SHA256:
4d5f3690cdff840ceba70c1b1630ceadd0d3dcf23c8e0add0257cba2f166f5e6SHA256: (code.exe)
b721ae3c71fb898a0876d6f2fde67628957d067110c0e0de35d74064a4d7f150SHA256: (notepad.exe)
44e5f8c6462688c6cce7f25b6790aa791f8e377d623896a41e6d6936ef0c29bdSHA256: (chrome.exe)
5a415f0b86c296e785b173a4e1525571b9fdd927f46f58c337b9de25d8bfebff
MITRE:
| Technique ID | Technique Name | Evidence |
|---|---|---|
| T1071.001 | Application Layer Protocol: Discord API | Uses Discord API to create channels and send C2 commands via Discord |
| T1059.001 | Command and Scripting Interpreter: PowerShell | Executes shell commands via PowerShell and processes their output |
| T1562.001 | Impair Defenses: Disable or Modify Tools | Patches Event Tracing for Windows (ETW) to evade detection |
| T1027 | Obfuscated Files or Information | Utilizes code and command obfuscation to conceal malicious actions |
| T1119 | Automated Collection | Automatically collects screenshots and data from infected device |
| T1041 | Exfiltration Over C2 Channel | Sends exfiltrated data over Discord C2 channel |
3) Floxif (Windows)
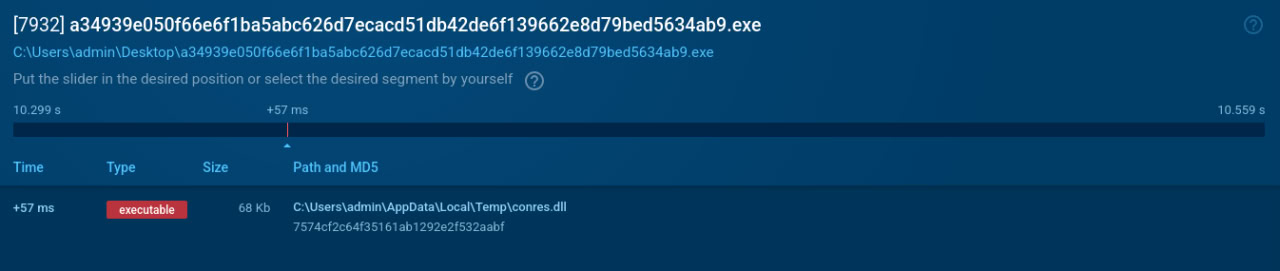
Sample: ANY.RUN
Floxif is backdoor malware that creates hidden access points for remote management and execution of attacker commands.
How to detect: Uses the associated DLL that the malware drops for malicious purposes.
Key facts:
- The malware has been active for several years, but new samples regularly appear.
Analytical note:
| Detected | External sources | Last Submission to ANY.RUN | Sandbox Evasion | VT First Submission |
|---|---|---|---|---|
| 2025-10-14 | News | 2025-10-17 | 100+ | 2025-10-10 |
With the following TI Lookup query, we can search through recent public sandbox analyses and identify this malicious activity.
filePath:"Temp\\conres.dll"
IOCs:
SHA256:
a34939e050f66e6f1ba5abc626d7ecacd51db42de6f139662e8d79bed5634ab9FIle path:
C:\\Users\\admin\\AppData\\Local\\Temp\\conres.dllSHA256: (conres.dll)
de055a89de246e629a8694bde18af2b1605e4b9b493c7e4aef669dd67acf5085Domains:
aieov.com, middlechrist.com, pywolwnvd.biz, cvgrf.biz, npukfztj.biz, ssbzmoy.biz, przvgke.biz, knjghuig.biz, qaynky.biz, bumxkqgxu.biz, dwrqljrr.biz, nqwjmb.biz, ytctnunms.biz, myups.biz, oshhkdluh.biz, yunalwv.biz, jpskm.biz, lrxdmhrr.biz, wllvnzb.biz, gnqgo.biz, jhvzpcfg.biz, acwjcqqv.biz, vyome.biz, yauexmxk.biz, iuzpxe.biz, sxmiywsfv.biz, vrrazpdh.biz, ftxlah.biz, typgfhb.biz, gvijgjwkh.biz, qpnczch.biz, brsua.biz, dlynankz.biz, oflybfv.biz, yhqqc.biz, mnjmhp.biz, opowhhece.biz, jdhhbs.biz, mgmsclkyu.biz, warkcdu.biz, gcedd.biz, jwkoeoqns.biz, xccjj.biz, apicoreservice.ru, qegyhig.com, vocyzit.com, lymyxid.com, galyqaz.com, vonypom.com, puzylyp.com, lysyfyj.com, lyvyxor.com, gahyqah.com, gadyniw.com, qetyfuv.com, freedesktopsoft.com
MITRE:
| Technique ID | Technique Name | Evidence |
|---|---|---|
| T1012 | Query Registry | Checks proxy server information |
| T1105 | Ingress Tool Transfer | Process drops executable |
| T1071 | Application Layer Protocol | Connects to the CnC server |
| T1027.002 | Obfuscated Files or Information: Software Packing | Uses UPX packer |
| T1497 | Virtualization/Sandbox Evasion | Uses functionality for VM detection |
| T1546 | Event Triggered Execution | Changes the AppInit_DLLs value (autorun option) |
Conclusion
1) Attacks are shifting to private trusted channels
Maverick uses WhatsApp, and ChaosBot leverages Discord for C2. Attackers are moving away from email and web platforms to environments with weaker filters and higher trust, increasing infection rates and making blocking more difficult.
2) Geofencing as standard anti-analysis
Triggers like IP=Brazil + language pt-BR in Maverick are now common. If sandboxes cannot simulate regional settings, some malware samples will never reveal their payloads, leading to missed detections.
3) Legacy malware remains dangerous
Floxif is still active, with over 100 missed detections. Legacy malware families continue to provide a strong return on investment for attackers.
4) Legitimate binaries as attack vectors
ChaosBot relies on DLL side-loading, including components related to Edge. Without strict integrity controls, attackers don’t need zero-day exploits, just the right folder and DLL name.
5) Telemetry under attack
ChaosBot patches EtwEventWrite and uses anti-VM techniques to blind monitoring. If you fail to detect attempts to disable telemetry, you are effectively blind to the attack.